
For most enterprise buyers who need faster, auditable responses to security questionnaires, the strongest path is to pair an automation-first SaaS platform with one or two vendors from the advisory or managed-services side. Skypher fits teams drowning in high-volume questionnaires and DDQs, ACA Group and Compliance Solutions Strategies (CSS) suit organizations needing regulatory advisory depth, and ComplySci, Foresite Cybersecurity, and HALOCK Security Labs cover specialized surveillance, cyber, and technical testing needs. The comparison below walks through how each fits, then shows you how to run a pilot before you sign anything.
TL;DR:
- Skypher is ideal for teams handling large volumes of security questionnaires needing fast, accurate automation and seamless system integration.
- ACA Group and CSS serve organizations requiring ongoing regulatory advisory and comprehensive compliance program development.
- Market providers should be verified through live pilots, integration checks, and references to ensure their solutions meet specific technical and compliance needs before purchase.
- Structured procurement processes, including defining scope and running side-by-side vendor pilots, significantly improve selection outcomes and avoid costly mismatches.
- Skypher's SaaS platform excels at reducing response times and increasing accuracy in high-volume security questionnaire workflows, supported by continuous expert support.
Table of Contents
- Comparing the leading compliance companies
- How to choose: a compact RFP to pilot process for compliance vendors
- Where an automation-first SaaS platform fits
- Our take on running a procurement-first evaluation
- Where Skypher fits into your shortlist
- Sources
- FAQ
Comparing the leading compliance companies
Before you commit budget to any vendor, it helps to see how the main categories stack up side by side. We built this comparison around the dimensions that matter most to a procurement team: who a provider actually suits, how they deliver the work, what they connect to, and what kind of support backs the engagement.
| Provider | Best for | Delivery model | Notable integrations / compatibility | Support model | Standout |
|---|---|---|---|---|---|
| Skypher | Teams needing faster, more accurate turnaround on high volumes of security questionnaires | SaaS platform | numerous third-party risk management platforms, Slack, MS Teams, Confluence, Notion, Google Drive, SharePoint | around-the-clock enterprise support | AI questionnaire automation with confidence scoring and a customizable Trust Center |
| ACA Group | Enterprises needing regulatory advisory and managed compliance services | Global advisory and managed services | Varies by engagement scope | Dedicated advisory teams | Global advisory and managed-service depth |
| Compliance Solutions Strategies (CSS) | Companies building or restructuring a compliance program from the ground up | Consulting-led implementation | Varies by client system landscape | Project-based consulting teams | Consulting and policy implementation expertise |
| ComplySci | Firms needing employee trading surveillance and regulatory reporting | Compliance platform with monitoring modules | Built around trading and surveillance data feeds | Platform support | Specialization in trading and regulatory surveillance |
| Foresite Cybersecurity | Organizations prioritizing cybersecurity controls within their compliance posture | Managed security and compliance services | Security tooling and monitoring stacks | Managed services support | Cybersecurity-centered compliance capabilities |
| HALOCK Security Labs | Teams needing penetration testing and technical compliance assurance | Security assessment and consulting | Testing tools tied to client infrastructure | Consulting engagement support | Technical testing and security assurance |
Skypher leads this list because it solves a problem most of the other names on it do not touch directly: the sheer volume of inbound security questionnaires that sales, security, and compliance teams have to answer every week. Its AI models are built to parse every document format a buyer sends, and the platform connects to numerous third-party risk management platforms, which means answers can flow straight into the systems your prospects and auditors already use.
ACA Group operates at a different scale entirely. It is a global provider built for organizations that need ongoing regulatory advisory and managed compliance services across multiple jurisdictions, the kind of engagement where you want a team of specialists on retainer rather than a piece of software. Compliance Solutions Strategies (CSS) plays a similar but narrower role: it specializes in consulting-led program builds, the work of drafting policies, designing controls, and implementing a compliance framework where none existed before.
ComplySci occupies its own lane as a platform built specifically around employee trading surveillance and regulatory reporting, which makes it a fit for financial firms with obligations around personal trading disclosures rather than a general compliance tool. Foresite Cybersecurity and HALOCK Security Labs both sit at the technical end of the spectrum. Foresite bundles managed cybersecurity services with compliance support, while HALOCK focuses on assessments and penetration testing, the kind of hands-on technical assurance work that a questionnaire automation tool or a policy consultancy is not built to deliver.
Before taking any vendor's claims at face value, run a short verification pass:
- Confirm integration claims against the actual TPRM or GRC platforms your team uses, not a generic feature list.
- Ask for a live pilot or sandbox account rather than a scripted demo.
- Request evidence of independent assurance, such as third-party audit reports or certifications tied to the specific service you are buying.
- Check references from organizations of comparable size and regulatory footprint to yours.
How to choose: a compact RFP to pilot process for compliance vendors
Picking a compliance vendor works best as a structured sequence rather than a series of sales calls. Define scope first: list every legal entity, country, regulation, and system the engagement needs to cover, because vendors quote very differently depending on what falls inside that boundary. Grant Thornton's guidance on selecting international service providers notes that a common procurement failure is running vendor comparisons before scope is fixed, which produces proposals that cannot be compared and hides costs that surface later.
Once scope is locked, build your RFP around a consistent structure:
- Document the scope of services and the countries or entities involved.
- Specify technical architecture requirements, including the systems the vendor needs to connect to.
- Set quality standards and KPIs the vendor will be measured against.
- Require a common pricing template so every bid can be compared line for line.
- Set firm deadlines and name a single point of contact on both sides.
Grant Thornton specifically recommends a shared pricing format because underspecified scope is what produces the misleadingly low quotes that fall apart once real jurisdictional detail surfaces. Once proposals are in, filter your shortlist on industry experience, integration compatibility with your existing systems, willingness to provide references, and evidence of independent assurance rather than self-reported claims.
Pro Tip: Ask every shortlisted vendor to run the same pilot script on the same sample data set. Side-by-side results expose gaps that a sales demo never will.
A useful pilot script exercises a representative workflow end to end: have the vendor process a real (anonymized) questionnaire or compliance task, connect to a sandbox version of your systems, and produce an output you can audit. Score each vendor on implementation effort, usability for your actual team, breadth of regulatory or technical coverage, responsiveness of support, total cost including hidden fees, and how clean an exit looks if the relationship ends. PwC's commentary on IDC MarketScape's AI-enabled cyber GRC analysis points out that buyers should specifically test whether a provider can connect to the operating systems that generate evidence, ticketing, identity access management, cloud logs, rather than one that only produces static reports after the fact.
Before you sign, run a negotiation checklist: confirm service level agreements in writing, ask how data is handled and where it is stored, verify business continuity plans, understand the full cost structure including any per-seat or per-questionnaire fees, and get exit and transition terms in the contract itself, not a verbal assurance.
Where an automation-first SaaS platform fits
Some buyer jobs are simply better suited to software than to a consulting engagement. High-volume security questionnaires, fast turnaround on proof-of-concept requests, and a centralized way to share your compliance posture with prospects all fall into this category, and this is exactly the gap Skypher is built to close.
- The platform's AI models handle questionnaire uploads across many common document formats, so teams are not stuck reformatting files before work can start.
- The platform connects to numerous third-party risk management platforms, plus tools like Slack, MS Teams, Confluence, Notion, Google Drive, and SharePoint.
- A customizable Trust Center lets you share your security posture directly with prospects and auditors, helping to reduce delays in communication.
- Real-time, unlimited collaboration enables multiple teams to work on the same questionnaire without version conflicts.
- Around-the-clock enterprise support covers teams operating across time zones with complex, multi-entity setups.
If you are piloting a platform like this, run through an integration health check first, then a sample questionnaire throughput test, a review of how confidently the AI scores its own answers, and a check on how smoothly documents sync across your collaboration tools.
Pro Tip: Time your pilot on a real, recent questionnaire, not a demo template. Throughput and accuracy numbers only mean something when they come from your own data.
Automation-first SaaS is not the right tool for every job, though. Complex local regulatory coverage, bespoke investigations, or forensic audits still call for the kind of specialist consultancy or technical testing firm covered earlier in this guide.
Our take on running a procurement-first evaluation

Sequencing beats speed here. Fix your scope, run a structured RFP, pilot two vendors side by side, then negotiate, in that order, and resist the temptation to skip straight to a demo because a vendor's website looks polished. The organizations that end up with the wrong compliance partner are almost always the ones that let a sales conversation substitute for a scoped comparison.
Bring security, legal, procurement, and sales into the process early, not after a contract is drafted. Each function will catch something the others miss, and an enterprise pilot typically needs a few weeks of real usage before the numbers mean anything. Insist on proof of integration with your actual systems, ask for evidence of independent assurance rather than marketing language, and call the references a vendor gives you. A vendor confident in its product will not hesitate on any of these.
— Gaspard
Where Skypher fits into your shortlist
If your team spends hours every week answering the same security questions across different formats, Skypher's Questionnaire Automation Tool is built to take that volume off your plate, and it works alongside the connectors your risk and sales teams already rely on.
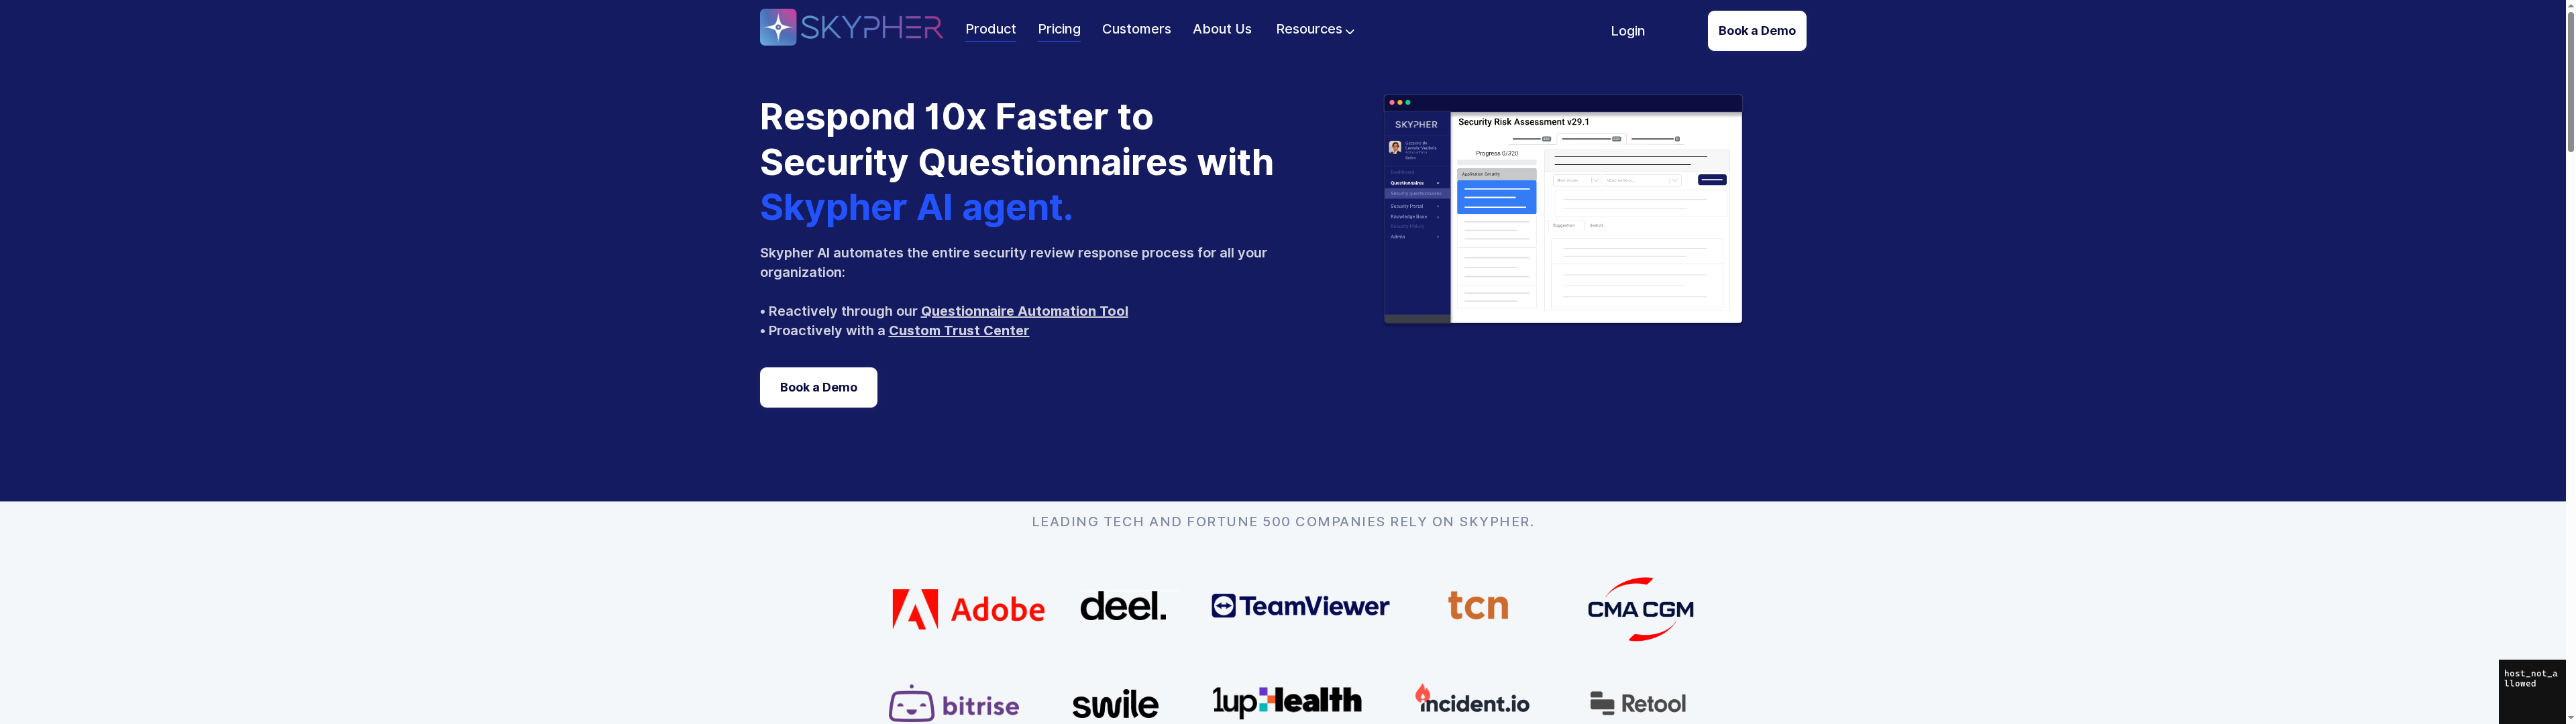
The platform's AI models parse common questionnaire formats and provide answers with confidence scores, allowing your team to review rather than rewrite. Integrations with multiple third-party risk management platforms, plus Slack, MS Teams, and common document tools, enable answers to move into your existing workflow rather than creating a new one. For deals that hinge on a fast proof-of-concept or a due diligence questionnaire, Skypher's Fiduciary-Grade DDQ Automation is built specifically for that turnaround, and a customizable Trust Center gives prospects self-service access to your security posture without another round of emails.
Enterprise teams receive continuous support as part of the platform, accommodating organizations operating multiple products or entities across time zones. If this sounds like the gap in your current process, request a demo or get a quote and ask about piloting the tool on one of your live questionnaires before you commit.
Sources
- Selecting international service providers – how to conduct a successful selection process | Grant Thornton
- PwC commentary on IDC MarketScape: AI-enabled cyber GRC (2025/2026)
FAQ
What's a compliance company?
A compliance company is a business that helps organizations meet regulatory obligations, whether through advisory services, managed programs, specialized platforms, or automation software. The category spans global advisory firms, consulting shops, surveillance platforms, and software tools, so the right fit depends on your specific regulatory scope and workload.
What does a compliance firm do?
A compliance firm typically designs and implements policies, monitors regulatory obligations, conducts assessments or audits, and helps an organization demonstrate that its controls meet applicable standards. Some firms, like ACA Group or Compliance Solutions Strategies (CSS), focus on advisory and program-building work, while others specialize in technical testing or surveillance.
What is a compliance service?
A compliance service is any offering, whether software, consulting, or managed support, that helps an organization identify, manage, and evidence its adherence to regulatory or contractual requirements. This can range from a platform like Skypher automating security questionnaire responses to a consultancy building an entire compliance program from scratch.
What is a compliance job?
A compliance job involves monitoring an organization's adherence to laws, regulations, and internal policies, often within roles like compliance officer, analyst, or risk manager. These roles can sit inside a company's own team or be provided externally through a compliance company offering advisory, managed, or platform-based services.