
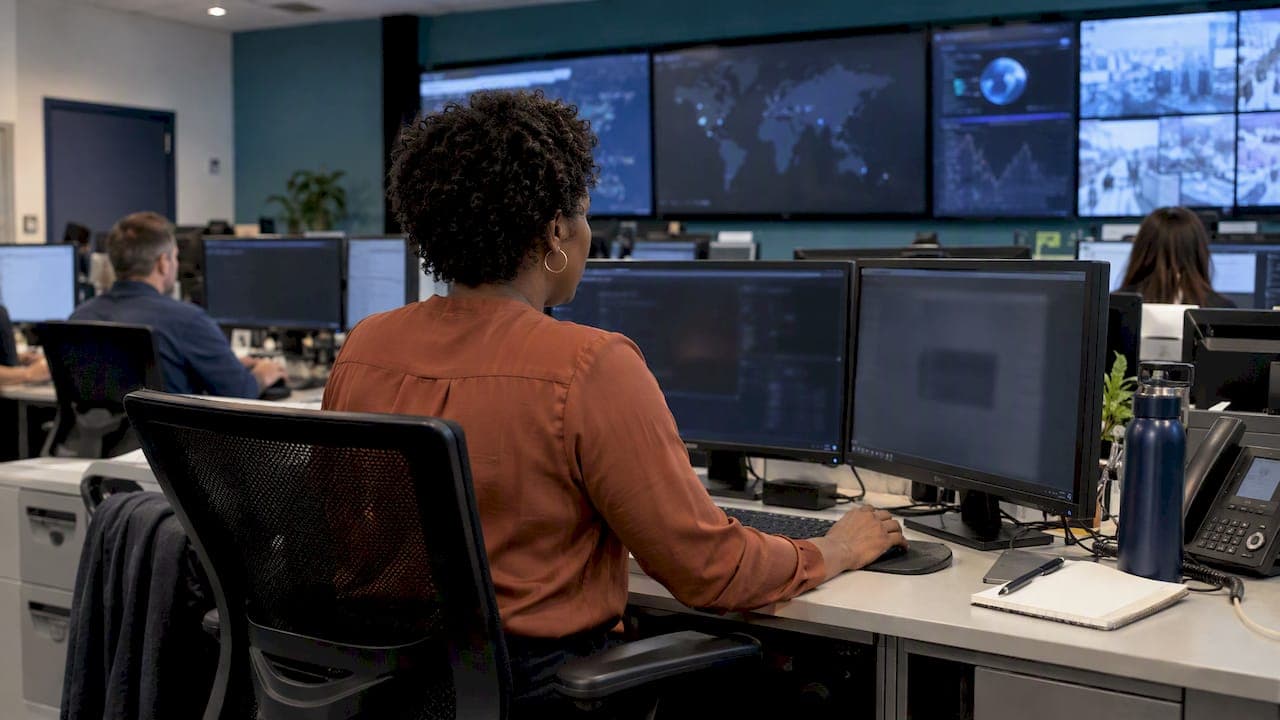
In security and IT, SOC stands for either Security Operations Center (the team and function that watches for cyber threats) or System and Organization Controls (the family of audit reports a CPA issues about a company's controls). In hardware it is System on a Chip, and in US labor statistics it is the Standard Occupational Classification. Which one you need depends entirely on where you saw the acronym.
We work with security, risk and compliance teams every day, and this is one of the most common sources of confusion we see. Below we walk through each meaning, show you how to tell them apart in context, and explain why the difference matters when a customer sends you a security questionnaire.
TL;DR
- Security Operations Center: the people, processes and technology that monitor, detect and respond to cyber threats, usually around the clock.
- System and Organization Controls: AICPA audit reports (SOC 1, SOC 2, SOC 3) produced by a licensed CPA, not a team or a room.
- Other meanings: System on a Chip (electronics) and Standard Occupational Classification (US federal job coding).
- In a questionnaire: "Do you have a SOC?" is ambiguous. Clarify whether the question means an operations center or an audit report before you answer.
Table of Contents
- The main meanings of SOC at a glance
- SOC as Security Operations Center
- SOC as System and Organization Controls
- SOC as System on a Chip
- SOC as Standard Occupational Classification
- How to tell which SOC someone means
- Why the difference matters in security questionnaires
- Our perspective: treat SOC answers as shared knowledge
- Put it to work: faster, consistent answers
- Related reading on SOC reports
- FAQ
- Sources
The main meanings of SOC at a glance
| Meaning | Field | What it is | Typical context |
|---|---|---|---|
| Security Operations Center | Cybersecurity | A team, facility or function that monitors and responds to threats | Incident response, MDR, security staffing |
| System and Organization Controls | Audit and compliance | Attestation reports on a service organization's controls | Vendor reviews, enterprise sales, questionnaires |
| System on a Chip (SoC) | Electronics | An integrated circuit holding a whole system on one chip | Phones, embedded devices, chip design |
| Standard Occupational Classification | US government, HR | A federal system for classifying jobs | Labor statistics, workforce reporting |
| Short for "social" or "society" | General language | A dictionary abbreviation, often lowercase | Sociology, older texts |
The Wikipedia disambiguation page for SOC lists many more niche uses, from medical dictionaries to engineering terms, but the four above cover nearly everything a business reader will meet.
SOC as Security Operations Center
This is the meaning most people searching the term in a business setting want. Microsoft describes a security operations center as a centralized function or team responsible for improving an organization's cybersecurity posture and for preventing, detecting and responding to threats. IBM adds a useful pronunciation note: the term is usually said as "sock," and the same piece describes a SOC as unifying and coordinating an organization's cybersecurity technologies and operations.
People, processes and technology
A SOC is not just a room full of screens and it is not just a software license. The SANS Institute's definition, quoted in a community guide to building a SOC, frames it as a combination of people, processes and technology protecting an organization's information systems. In practice that means:
- People: analysts who triage alerts, threat hunters, incident responders and a manager who owns the function.
- Processes: playbooks, escalation paths, shift handovers and post-incident reviews.
- Technology: log collection, a SIEM, endpoint detection, threat intelligence feeds and case management.
If you want a concrete picture of what those threats look like for an ordinary business, this overview of examples of cyber risks (in Dutch) shows the kinds of incidents a SOC exists to catch.
How a SOC is measured
The quality of a SOC is judged by outcomes rather than tool count. nFlo's glossary entry points to operational measures such as Mean Time to Detect (MTTD) and Mean Time to Respond (MTTR). A SOC with twenty tools and a slow response is weaker than a lean one that finds and contains incidents quickly.
SOC versus NOC
A Network Operations Center (NOC) is a different function. The NOC watches availability and performance, such as uptime and latency, while the SOC focuses on security. The same nFlo glossary argues that merging the two in larger organizations can cause security incidents to be mistaken for performance problems. Treat that as one expert's view rather than a universal rule, but the separation of concerns is a sound starting point.
In-house, outsourced or hybrid
Not every company runs its own SOC. Smaller organizations often buy the function as a managed service, and larger ones may run a hybrid model with an internal team by day and a provider overnight. The right choice depends on your staffing, your data sensitivity and your regulatory obligations. What matters for the rest of this article is that a SOC in this sense is something an organization operates.
SOC as System and Organization Controls
The second meaning is the one that fills the inboxes of security and compliance teams. According to the AICPA, System and Organization Controls is a suite of service offerings that CPAs may provide in connection with the system-level controls of a service organization. In other words, a SOC report is a document, and it is written by an independent auditor.
The suite originally appeared as three report types. An ISACA Journal article describes the AICPA introducing Service Organization Controls reports, identified as SOC 1, SOC 2 and SOC 3.
SOC 1, SOC 2 and SOC 3 in plain terms
- SOC 1 covers controls relevant to a customer's financial reporting. Think payroll processors or payment platforms.
- SOC 2 covers controls tied to trust services criteria such as security, availability and privacy. This is the report most software buyers ask for.
- SOC 3 is a general-use summary of a similar assessment that can be shared publicly.
For a deeper comparison, we wrote about the key differences between SOC 1 and SOC 2, and if you are weighing which attestation your own company needs, our SOC 2 compliance requirements guide covers the criteria step by step.
Type 1 versus Type 2
Both SOC 1 and SOC 2 reports come in two types. A Type 1 report describes the design of controls at a single point in time. A Type 2 report goes further and tests whether those controls operated effectively over a period. Most enterprise buyers prefer Type 2 because it shows behavior over time rather than a snapshot. Our complete guide to SOC Type II reports explains what auditors test and how to read the result.

A report is not a certification
People often say a company is "SOC 2 certified." Strictly speaking, a SOC 2 is an attestation report issued by a CPA firm, not a certificate granted by a regulator. The wording matters in questionnaires and contracts, so we recommend using "has a SOC 2 Type 2 report" and stating the audit period.
If you want to see what one looks like before requesting your own, our walkthrough of a SOC 2 sample report highlights the sections security teams should read first.
SOC as System on a Chip
In electronics the acronym is often written SoC, with a lowercase "o." PCMag's definition is not needed here; the idea is simple. A system on a chip is an integrated circuit that puts the components of a computer or other electronic system, such as the processor, memory and input and output interfaces, on a single chip. Smartphones, tablets and many embedded devices rely on this design because it saves space and power.
If you read "SoC" next to words like "ARM," "core," "firmware" or "die," you are in hardware territory, and the security and audit meanings do not apply.
SOC as Standard Occupational Classification
The fourth meaning belongs to HR and statistics. The Bureau of Labor Statistics maintains the Standard Occupational Classification, a federal system that statistical agencies use to classify workers and jobs so that data is comparable across the economy. The BLS describes the current structure as 867 detailed occupations in 23 major groups.
One detail trips up many HR teams: the code follows the work performed, not the job title. A person with a technical title who spends most of their time managing people is coded in a management category. If you complete labor, diversity or workforce reports, check the 2018 SOC Manual for the definitions before assigning codes.
How to tell which SOC someone means
We suggest three quick checks.
- Look at the sender. A recruiter, HR system or government form points to the occupational classification. An engineer or procurement contact points to the chip or the audit.
- Look at the verb. "Run a SOC," "staff a SOC" and "outsource our SOC" describe an operations center. "Provide a SOC," "share your SOC" and "renew our SOC" describe a report.
- Look at the number. "SOC 1," "SOC 2" and "SOC 3" are always audit reports. "Tier 1 SOC analyst" is always the operations center.
When the context does not settle it, ask. A one-line clarification costs less than an incorrect answer that sits in a customer's vendor file for a year.
Why the difference matters in security questionnaires
Security questionnaires are where the two main meanings collide. A buyer might ask, "Do you have a SOC?" and one respondent will describe their 24/7 monitoring team while another attaches a SOC 2 Type 2 report. Both answers are honest, and both may miss what the buyer wanted to know.
The guidance is simple:
- If the question names a report, answer with the report type, the audit period, the auditor and any exceptions noted.
- If the question names monitoring, answer with your coverage hours, tooling, escalation process and response targets.
- If the question is ambiguous, answer both briefly and say which is which. For example: "We hold a SOC 2 Type 2 report covering [period]. Our security operations are staffed [coverage model]."
We have written separately about how security teams should read SOC as AICPA attestations and ask for SOC 2 Type 2, which is a good companion if you are on the buying side.
Consistency across answers
The larger risk is inconsistency. If one questionnaire says your SOC is in-house and another says it is outsourced, a reviewer will notice. Keeping a single, versioned source of truth for answers about both your operations center and your audit reports prevents contradictory statements from reaching customers.

Our perspective: treat SOC answers as shared knowledge
We see the same pattern at many B2B software companies. The compliance lead knows the audit period, the security lead knows the monitoring model, and the sales engineer has to answer a prospect on Friday afternoon. When each person answers from memory, the word "SOC" gets used loosely and answers drift.
Our view is that the acronym problem is really a knowledge management problem. The approach we recommend has four parts:
- Write down both definitions in your own terms. Keep one approved answer for "SOC as report" and one for "SOC as operations."
- Version your source documents. When a new SOC 2 report is issued, the previous period's answers should be retired, not left in circulation.
- Let AI draft, and let people verify. Our retrieval-based AI draws answers from your own knowledge base and shows a confidence score, so a reviewer can focus on low-confidence items rather than rereading everything.
- Share proof proactively. A customer-facing trust page answers the "which SOC" question before it is asked.
We would rather you spend an hour defining terms once than a day correcting them later. Please feel free to reach out if you would like to see how this looks in practice.
— Gaspard
Put it to work: faster, consistent answers
If your team receives questionnaires that ask about SOC reports, operations centers or both, our Questionnaire Automation Tool can parse the document in any format, draft answers from your approved content and route uncertain ones to the right colleague. To publish your SOC 2 status and related documents where customers can find them without asking, take a look at our Trust Center. For due diligence questionnaires in finance, see our DDQ automation. Pricing is quote-based, so the quickest way to get a figure is to contact us for a quote.
Related reading on SOC reports
If the audit meaning is what brought you here, these pages go deeper:
- SOC 2 compliance guide for tech and finance
- SOC 1 Type 2 reports and compliance workflow
- A SOC 1 report example
- SSAE 18 automation for SOC 2 preparation
FAQ
What does SOC stand for in cyber security?
In cybersecurity it usually stands for Security Operations Center, the team, processes and tools that continuously monitor for and respond to threats. In vendor assurance it often means System and Organization Controls, the AICPA audit reports. Read the surrounding words to see which one applies.
What does SOC stand for in software?
For software companies, SOC most often refers to a SOC 2 report, which customers request to evaluate a vendor's security controls. It can also mean the vendor's security operations center. In chip and embedded work, SoC means system on a chip.
How do you pronounce SOC?
In security, people usually say "sock," as IBM notes. For the chip meaning, many writers spell out the letters, saying "S-O-C." Audit reports are typically called "sock two" or "S-O-C two" depending on the speaker.
Is a SOC report the same as a security operations center?
No. A SOC report is a document issued by a licensed CPA about a company's controls. A security operations center is a team or function that monitors threats. A company can have one without the other, so questionnaires should specify which they mean.
What does SOC stand for in government and HR?
It stands for Standard Occupational Classification, the federal system the BLS maintains to classify jobs for statistical purposes. Codes are assigned by the work performed, not by the job title.
Sources
- Microsoft Security: What Is a Security Operations Center
- IBM: What Is a Security Operations Center
- nFlo: SOC glossary
- SANS-based guide: Security Operations Center in a Box
- AICPA: System and Organization Controls suite of services
- ISACA Journal: Understanding the New SOC Reports
- Wikipedia: SOC
- BLS: Standard Occupational Classification
- 2018 SOC Manual